

 iscover


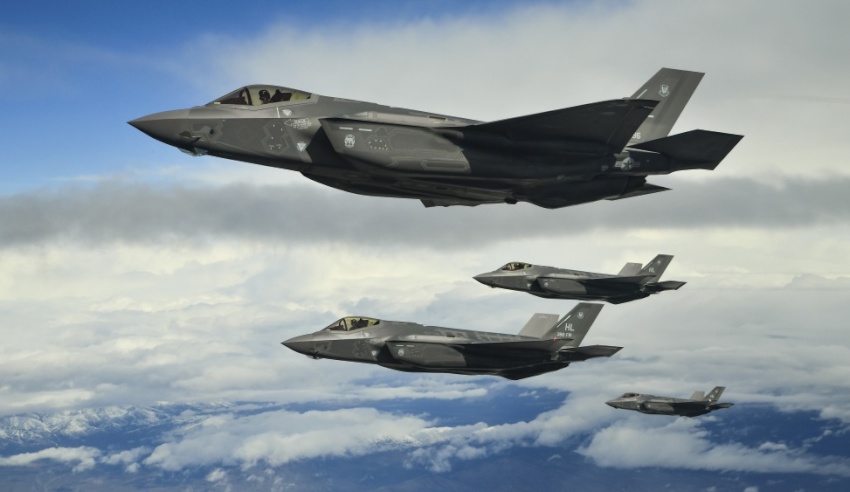
Restricted technical information of the F-35 Joint Strike Fighter (JSF), Australian naval vessels and defence aircraft was stolen from an Australian defence contractor last year.
Following the reveal of the theft yesterday with the release of the Australian Cyber Security Centre's annual threat report, Australian Signals Directorate (ASD) incident response manager Mitchell Clarke gave a presentation at the Australian Information Security Association (AISA), revealing ASD was alerted to the hack of the defence contractor by a "partner organisation".
Along with the F-35 and naval vessels, restricted technical information on the P-8 Poseidon, C-130 and the Joint Direct Attack Munition (JDAM) guidance kit was also stolen by the intruder.
The cyber thief was able to gain access to the network of the 50-person aerospace engineering firm that had been subcontracted by the Department of Defence.
"The company ... is very small, they run their own network, it's a network that's supported by one IT person. The rest of the company is either engineering staff or support staff to the engineering workforce," Clarke said.
The stolen information fell under the International Traffic in Arms Regulations (ITAR), a US regulatory regime that restricts and controls the export of defence and military related technologies.
In his highly detailed presentation, Clarke explained that the hacker had been in the network since at least mid July 2016, with data extrusion commencing roughly two weeks later.
Disturbingly, Clarke's presentation also revealed the hacker had minimal trouble gaining access to the information, explaining that, while the defence contractor's network was small and vulnerable to threats, the ASD investigation found that its internet-facing services still had their default passwords, admin::admin and guest::guest.
Audio of conference obtained via Stilgherrian/ZDNet.

Want to see more stories from trusted news sources?
Make Defence Connect a preferred news source on Google.
Click here to add Defence Connect as a preferred news source.